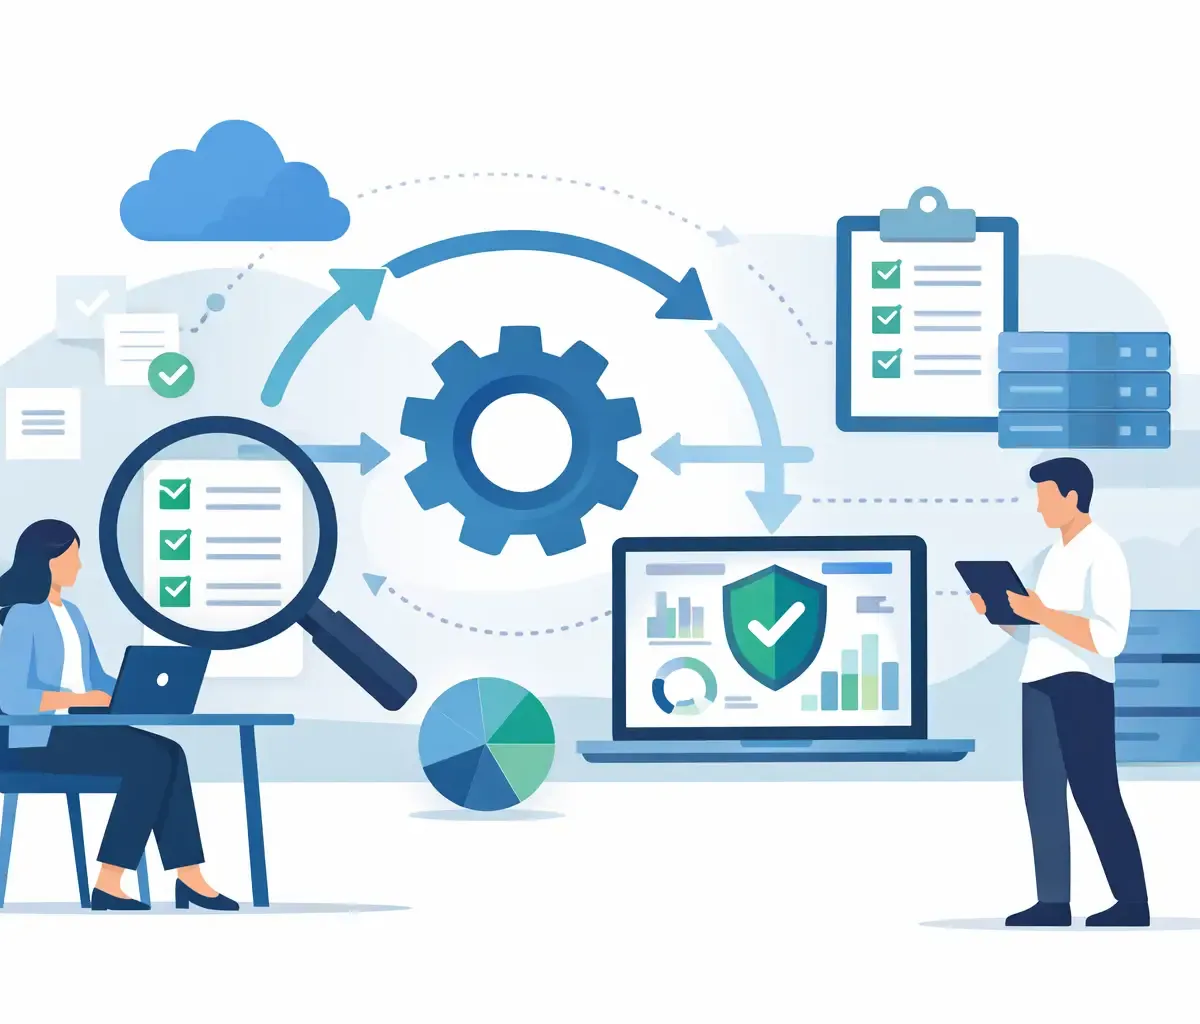
Audit requests rarely arrive at a convenient time. A regulator, customer or internal auditor asks for proof that a control operated over a defined period, and teams begin exporting reports, reconciling spreadsheets and chasing system owners. Learning how to automate audit evidence changes that cycle. The aim is not to produce more reports. It is to maintain credible, time-stamped proof of what was connected, configured, exposed and remediated before the audit begins.
For organisations with hybrid infrastructure, cloud services, Microsoft 365, Active Directory and operational technology, manual evidence collection creates a serious assurance gap. By the time a screenshot has been requested, created, reviewed and filed, the environment may have changed. Continuous evidence gives security, IT and leadership a defensible view of control performance without turning every audit into a short-notice project.
Why manual evidence gathering breaks down
Most audit evidence is distributed across tools that were bought for separate operational purposes. Asset inventories sit in one system, vulnerability findings in another, cloud configuration data elsewhere and identity records in a directory service. Each may be useful in isolation, but none answers the auditor's central question on its own: can you prove that the control was operating, across the relevant scope, during the period under review?
Spreadsheets create further risk. They rely on people to export the right data, preserve the correct filters, use consistent definitions and record exceptions. They are difficult to validate months later, particularly when asset ownership, IP addresses, user accounts or service dependencies have changed. A polished spreadsheet may be accepted as evidence, but it is rarely the strongest evidence available.
The operational cost is equally significant. Security teams lose time assembling packs instead of reducing risk. Control owners receive repeated requests for the same information. Senior leaders get retrospective assurance, often after a gap has already become a finding. Automation should reduce that friction while improving the quality and traceability of the evidence.
How to automate audit evidence from the source
The strongest approach starts with data that reflects the actual environment, not a manually maintained interpretation of it. Establish continuous visibility across the assets, identities, services and configurations that fall within the audit scope. This is the foundation for proving both coverage and control operation.
An agentless, scanless approach can be particularly valuable where endpoint agents are difficult to deploy, networks are sensitive or frequent scanning is operationally disruptive. It can bring network, cloud and identity intelligence together without creating another collection of disconnected reporting tools. The right method depends on the estate, however. Some technical controls still require endpoint telemetry or specialist logs. The priority is to make those sources visible through one assurance view rather than asking auditors to accept a patchwork of exports.
Define evidence by control objective, not by tool
Do not begin with a list of reports each security product can generate. Begin with the control objective. For example, a requirement to manage vulnerabilities may need proof that relevant assets were identified, assessed, prioritised, assigned and remediated within the agreed timeframe. A vulnerability dashboard alone is not enough if it cannot show the affected business service, the accountable owner or the history of remediation.
For each material control, document what good evidence looks like. It should show the population in scope, the test or policy applied, the result, any exceptions, the action taken and the date each fact was recorded. This makes evidence repeatable and allows internal audit to test the same logic each period.
Build a reliable scope first
Automation cannot compensate for unknown assets. If a device, account, cloud workload or exposed service is missing from the inventory, a control may appear effective simply because it was never tested. That is why discovery and service context belong at the start of the evidence process.
Create a living scope that identifies what is connected, who owns it, what service it supports and whether it is subject to a particular control. Grouping evidence by critical business service is more useful than grouping it only by technical domain. A board or auditor can then see whether a configuration weakness affects a low-value test system or a service that supports patient care, payments or public-facing operations.
Turn control checks into continuous evidence
Once the scope is reliable, automate the checks that demonstrate control performance. These may include secure configuration baselines, privileged account reviews, unsupported software, external exposure, encryption status, patch compliance and vulnerability remediation. The control should run on a defined schedule or continuously where the data source allows it.
Each check needs a clear pass, fail or exception outcome. Avoid controls with vague statuses such as review required unless a named owner, due date and decision trail sit behind them. An auditor does not need a claim that an issue was seen. They need evidence that the organisation identified it, assessed the risk and either fixed it or accepted it through an appropriate process.
A useful automated evidence record contains four distinct elements:
- the assets, users or services assessed, including those excluded from scope;
- the control criteria and policy version applied at the time;
- the results, exceptions and risk priority, with business-service context where available;
- the remediation, approval or risk acceptance trail, including ownership and timestamps.
This structure reduces arguments over what a report means. It also enables a sample-based audit to be answered quickly, because the evidence is connected to the underlying object rather than copied into a static document.
Preserve history, not just the latest status
A common mistake is to automate a current-state dashboard and call it audit evidence. Current status matters operationally, but audits often ask what was true at a point in time or across a period. A device that is compliant today may have been non-compliant for six weeks. A privileged account removed yesterday may have remained active throughout the review period.
Evidence automation therefore needs historical retention and timestamped change records. Preserve when an asset was first seen, when its risk state changed, when an exception was raised and when remediation was verified. Where a control result changes, retain both the previous and new result. This creates an evidence trail that can support ISO 27001, Cyber Essentials, customer assurance questionnaires and sector-specific obligations without recreating the past from memory.
Retention periods should reflect regulatory, contractual and internal policy requirements. More data is not automatically better. Retaining irrelevant technical detail can make disclosure and review harder. Focus on records that demonstrate scope, operation, exceptions and accountable decisions.
Make exceptions visible and governed
No mature environment has zero exceptions. Legacy platforms, clinical systems, specialist applications and third-party services may not meet every configuration standard immediately. Attempting to hide those exceptions weakens trust. Managing them openly strengthens assurance.
Automate the workflow around exceptions so that each one is tied to an owner, business rationale, compensating control, review date and approval authority. Escalate exceptions that are overdue or affect critical services. This turns an audit finding waiting to happen into an operational risk decision that leadership can understand.
The same principle applies to false positives and data-quality issues. If a source is temporarily unavailable or an asset cannot be classified, record the limitation and assign ownership. Evidence that acknowledges a known gap is more credible than a report that implies complete coverage where none exists.
Produce audit packs without creating a reporting factory
Automated evidence does not mean sending every auditor unrestricted access to a security platform. Auditors need clear, relevant material, while security teams need to protect sensitive operational data. Build role-appropriate evidence packs that combine control status, scope, exceptions and supporting history for the review period.
Use consistent reporting periods and definitions across IT, security and compliance. If one report counts a dormant account after 30 days and another after 90, the resulting discrepancy becomes an audit distraction. A single control library and shared data model reduce this risk, especially for MSPs and MSSPs managing assurance across multiple customers.
Rebasoft can support this model by bringing asset, service, vulnerability, configuration and identity intelligence into a single assurance environment. The practical value is not another dashboard. It is the ability to show what is affected, why it matters and what has been done, with evidence that can be reviewed by technical teams and leadership alike.
Measure the outcome, not only the automation
Track whether automation is reducing audit effort and improving control confidence. Useful measures include the time taken to fulfil an evidence request, percentage of assets with an accountable owner, number of overdue exceptions, evidence coverage for critical services and the age of high-risk unresolved findings. These measures demonstrate whether assurance is becoming more reliable, not merely more automated.
Start with the controls that consume the most manual effort or create the greatest business exposure. Prove the model over one audit cycle, refine the evidence criteria with internal audit, then extend it to adjacent controls. The result is a calmer audit process and leadership answers they can trust when the next assurance question arrives.