
From the Rebasoft blog.
Practical thinking on vulnerability management, asset intelligence, secure configuration and cyber resilience. 77 articles.
Privileged Access Review Guide for Clearer Control
This privileged access review guide shows security leaders how to find, assess and evidence high-risk access while keeping essential services running.
Read article
Audit Evidence Automation That Stands Up to Scrutiny
Audit evidence automation replaces last-minute evidence hunts with continuous, traceable proof of control performance, risk and business impact clearly.
Read article
Audit Evidence Requirements That Stand Up
Meet audit evidence requirements with continuous, service-led visibility that reduces effort, validates controls and gives leadership answers they trust.
Read article
How to Assess Cyber Resilience With Evidence
Learn how to assess cyber resilience with continuous evidence, business-service context and priorities that strengthen recovery, assurance and decisions.
Read article
How to Secure Microsoft Tenants with Confidence
Learn how to secure Microsoft tenants with clear controls, continuous evidence and risk-based priorities for stronger resilience and audit readiness now.
Read article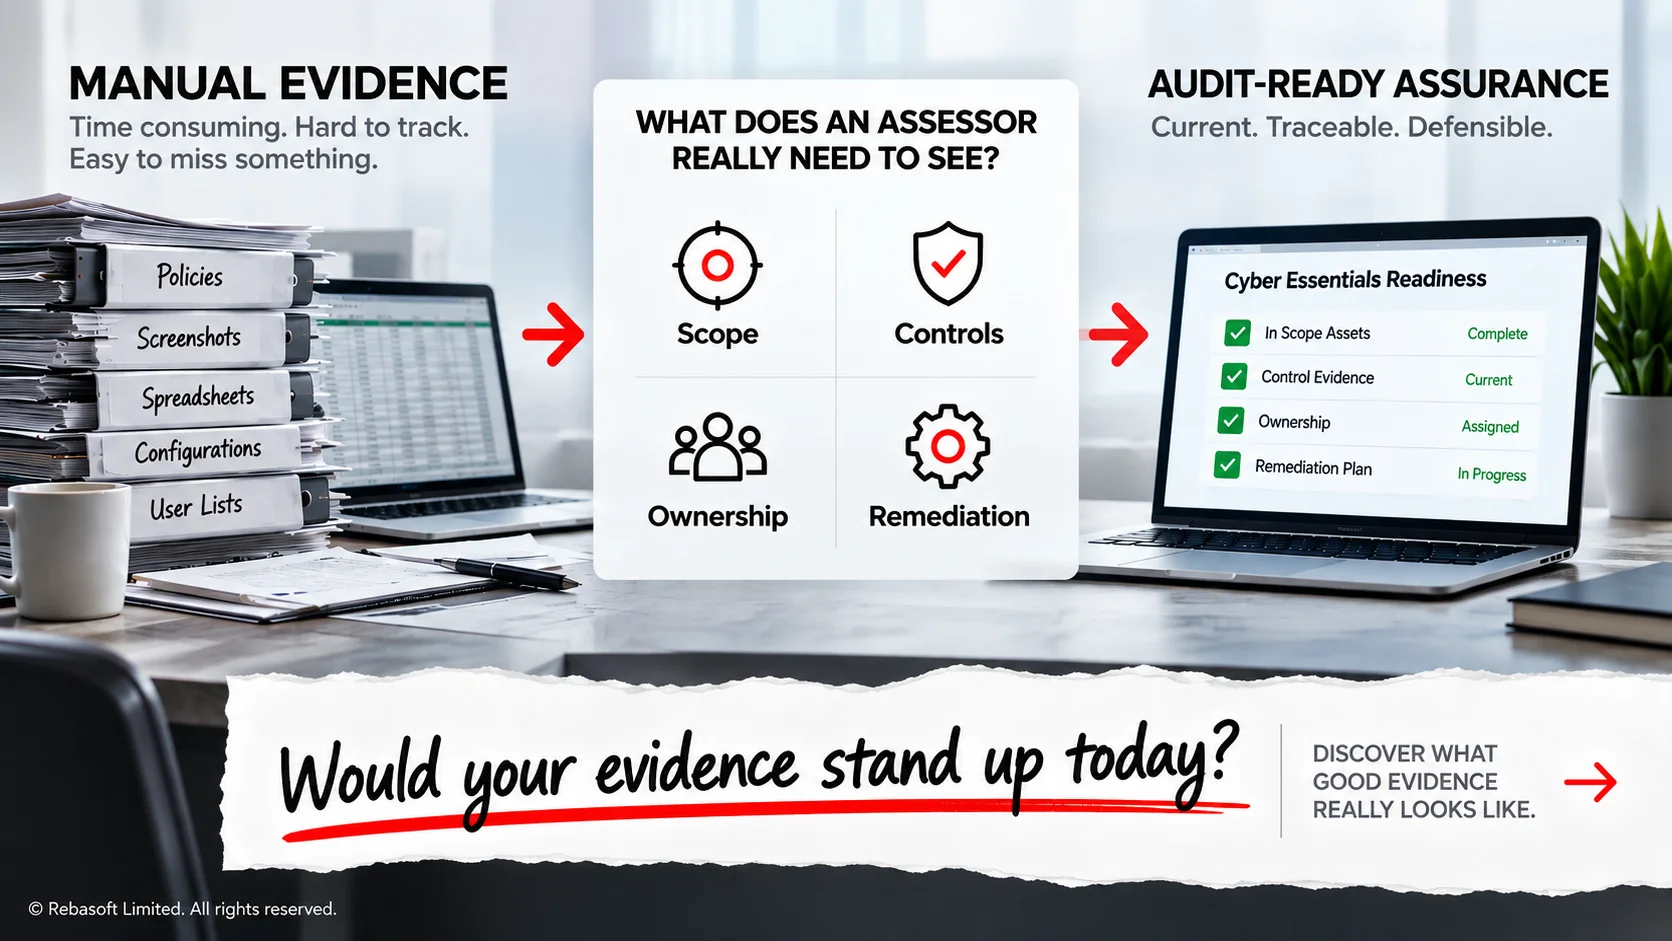
A Cyber Essentials Evidence Example That Stands Up
See a practical cyber essentials evidence example and learn how continuous asset, configuration and access data can reduce audit effort and risk at scale.
Read article
Business Context Risk Scoring That Drives Action
Business context risk scoring connects technical exposure to critical services, helping leaders prioritise fixes, evidence control and reduce cyber risk.
Read article
How to Document Security Controls That Stand Up
Learn how to document security controls with clear ownership, live evidence and service context to reduce audit effort and give leaders reliable assurance.
Read article
Identity Governance Software That Proves Control
Identity governance software gives leaders clear evidence of who has access, why it is needed, and where control gaps create business risk reliably.
Read article
How to Quantify Cyber Risk With Business Context
Learn how to quantify cyber risk using asset, service and control evidence, so leaders can prioritise remediation, resilience and investment confidently.
Read article
Choosing the Best OT Asset Discovery Approach
Find the best OT asset discovery approach for safe, continuous visibility across industrial networks, with business context, evidence and priorities.
Read article
How to Validate Security Controls With Evidence
Learn how to validate security controls using continuous evidence, service context and clear ownership to reduce cyber risk and audit effort across estate.
Read article
NIST CSF Implementation Guide That Delivers Evidence
A practical NIST CSF implementation guide for turning asset visibility, control evidence and service context into measurable cyber assurance at scale.
Read article
What a Microsoft Security Review Should Reveal
A Microsoft security review should reveal more than configuration gaps. Learn how to link Microsoft 365, Azure and identity risk to services and action.
Read article
Compliance Assurance Software That Proves Control
Compliance assurance software gives leaders real evidence of controls, exposes gaps by business service and reduces audit effort, cost and uncertainty.
Read article
Compliance Automation That Stands Up to Audit
Compliance automation turns continuous visibility into defensible evidence, reduces audit effort and helps leaders focus remediation on business risk.
Read article
Cyber Essentials versus ISO 27001 Compared
Cyber Essentials versus ISO 27001: compare scope, cost, assurance and operational effort to choose the right route for your organisation's risk strategy
Read article
Best Secure Configuration Software for Control
Choose the best secure configuration software with continuous evidence, asset context and clear prioritisation for faster audits and lower cyber risk.
Read article
Microsoft 365 Hardening Guide for Real Risk
A practical Microsoft 365 hardening guide for reducing exposure, proving controls and prioritising the actions that protect critical services first, fast.
Read article
Network Visibility Software That Proves What Matters
Network visibility software gives security and IT teams a clear view of assets, services and exposure, so they can prioritise risk and prove controls daily.
Read article
How to Automate Audit Evidence Without Chasing Spreadsheets
Learn how to automate audit evidence with continuous asset, identity and control visibility, reducing manual effort and giving auditors answers they trust.
Read article
How to Classify Assets for Better Cyber Risk
Learn how to classify assets by service, owner and criticality, helping teams prioritise cyber risk, speed audits and give leaders evidence they trust.
Read article
Cyber Essentials vs CE Plus: Which One Fits?
Cyber Essentials vs CE Plus explained: compare assessment, assurance, cost and evidence requirements to choose the right route for your organisation.
Read article
Vulnerability Management Platform Review Criteria
A vulnerability management platform review that cuts through alert volume, tests business context, evidence, coverage, and operational value at scale.
Read article
Essential Cyber Insurance Controls That Matter
Essential cyber insurance controls help organisations reduce loss, evidence security performance and secure cover on terms leadership can defend daily.
Read article
Agentless Discovery Versus Network Scanning
Agentless discovery versus network scanning: compare coverage, risk, operational impact and evidence quality to choose the right visibility model today.
Read article
How to Identify Shadow IT Before It Becomes Risk
Learn how to identify shadow IT using identity, network and service evidence, then prioritise exposures threatening operations, compliance and resilience.
Read article
How to Inventory Cloud Assets Without Blind Spots
Learn how to inventory cloud assets with continuous discovery, ownership and service context, so teams can prioritise risk, prove control and act faster.
Read article
What a Cyber Risk Platform Must Show Leaders
A cyber risk platform turns asset, identity and control data into clear priorities, continuous evidence and leadership answers boards can trust.
Read article
How to Reduce Attack Surface Without Losing Control
Learn how to reduce attack surface with continuous asset visibility, service context and evidence-led controls that cut risk and improve resilience today.
Read article
Security Tool Consolidation That Reduces Risk
Security tool consolidation reduces cost and noise while giving teams the asset, service and risk evidence needed to act with confidence each working day.
Read article
Asset and Service Intelligence Guide for Risk
Use this asset and service intelligence guide to find exposure, prioritise risk by business service, improve audit evidence and act with confidence daily.
Read article
Asset Intelligence Platform for Clearer Risk
An asset intelligence platform gives security and IT leaders continuous evidence on assets, services and exposure, so they can act on risk with confidence.
Read article
Cyber Essentials Plus Readiness That Stands Up
Cyber Essentials Plus readiness starts with clear asset, identity and configuration evidence. Build assurance that reduces audit effort and risk materially.
Read article
How to Prioritise Cyber Exposure with Confidence
Learn how to prioritise cyber exposure with asset, service and control context to reduce risk, prove assurance and speed better decisions every time.
Read article
Agentless vs Agent Based Security Compared
Agentless vs agent based security shapes visibility, cost and resilience. See where each approach fits and how to build reliable, continuous assurance.
Read article
Secure Configuration Management Guide for Leaders
This secure configuration management guide shows how to reduce exposure, validate controls continuously and prioritise fixes by business service impact.
Read article
How to Discover Unknown Assets Across Your Estate
Learn how to discover unknown assets across your estate, prioritise exposure by service impact, and produce evidence leaders and auditors can trust now.
Read article
Vulnerability Management Lifecycle Guide
This vulnerability management lifecycle guide shows how to find, prioritise and fix exposure with service context, continuous evidence and clear ownership.
Read article
Vulnerability Management vs Patch Management
Vulnerability management vs patch management: learn how each reduces risk, where patching falls short, and how to prioritise remediation with confidence.
Read article
7 Best Microsoft 365 Posture Tools Compared
Compare the best Microsoft 365 posture tools for continuous control assurance, clear risk prioritisation and audit evidence that leadership can trust.
Read article
Microsoft 365 Security Posture Review Explained
A Microsoft 365 security posture review exposes control gaps, reduces audit effort and gives leaders evidence to prioritise cyber risk with confidence.
Read article
Continuous Control Validation That Proves Assurance
Continuous control validation gives security teams live evidence that controls work, reduces audit effort and focuses remediation on business risk first.
Read article
What Is an Intelligence Asset in Cybersecurity?
What is an intelligence asset? Learn how it turns raw asset data into business context, better prioritisation, and stronger cyber assurance.
Read article
What Asset Intelligence Services Actually Deliver
Asset intelligence services give organisations clear, continuous visibility of assets, users and services so teams can reduce risk faster.
Read article
Secure Configuration That Reduces Risk
Secure configuration reduces cyber risk, cuts audit effort and gives teams clear, continuous evidence across cloud, identity and on-prem estates.
Read article
Secure Configuration Guide for Real Risk
A secure configuration guide for CISOs and IT leaders who need clearer priorities, stronger assurance, and faster evidence across complex estates.
Read article
Secure Configuration Management That Works
Secure configuration management reduces cyber risk, cuts audit effort, and gives leaders clear evidence that critical systems are configured properly.
Read article
7 Vulnerability Management Examples That Matter
See 7 vulnerability management examples that show how to prioritise risk, cut audit effort, and give leadership answers they can trust.
Read article
Vulnerability Management Tools That Cut Noise
Vulnerability management tools should reduce risk, not add noise. Learn what matters most in coverage, context, prioritisation and proof.
Read article
Best Vulnerability Management Software
Best vulnerability management software should do more than scan. Learn how to choose a platform that cuts risk, proves control and saves time.
Read article
What Makes a Vulnerability Management Program Work
A vulnerability management program should cut noise, prioritise real risk, and give leaders evidence they can trust across assets and services.
Read article
Vulnerability Management Lifecycle Explained
Understand the vulnerability management lifecycle, from discovery to remediation and reporting, with clear steps that reduce cyber risk.
Read article
What Is Vulnerability Management?
What is vulnerability management? Learn how organisations find, prioritise and fix exposures faster with business context and clear risk ownership.
Read article
Why Vulnerability Management Is Difficult and Expensive
If your organisation uses IT, you face identical cyber risks as Fortune 500 companies. Here is how vulnerability management becomes more effective.
Read article
Improved Cyber Security Using Asset Intelligence
A short overview for CIO/CTO/CISO management looking to improve cyber security defences. If you can see it, you can secure it.
Read article
How Rebasoft Maps to NIS2
NIS2 mandates operators of essential services and digital service providers to implement robust security. Here are 7 ways Rebasoft helps you comply.
Read article
The Risks of Over-Relying on Large Software Companies: A Cyber Security Perspective
Large software vendors offer robust, scalable solutions, but over-dependence on a single vendor can undermine the efficiency and security you seek.
Read article
DORA: What Is It and Why Should You Care?
DORA is an EU regulation to enhance the cyber resilience of the financial sector, applying from 17 January 2025. Here's what it means and how to comply.
Read article
You should update your servers now
A high-severity OpenSSH vulnerability (CVSS 7.0) could allow remote code execution on unpatched servers. Here's what's affected and how to fix it.
Read article
NIS2: Why Should You Care?
NIS2 is an EU cyber security directive that member states must adopt into law by 18 October 2024. Here's why it will impact organisations well beyond the EU.
Read article
Embracing the Future of Vulnerability Management: Insights for IT Security Leaders
Three pivotal trends shaping the future of Vulnerability Management, and how Rebasoft's unified platform helps IT security leaders address them effectively.
Read article
IT Hardware, Software & Vulnerability Audit: Not Just for Christmas
Businesses rely on IT infrastructure, but rising cyber threats demand a robust security strategy built on comprehensive hardware and software audits.
Read article
The Critical Role of Vulnerability Management in Network Security Strategy
Robust network security demands a proactive approach. Vulnerability management addresses weaknesses before they can be exploited and keeps you compliant.
Read article
Misconceptions about Vulnerability Management
Vulnerability management is vital but tricky, giving rise to dangerous misconceptions. Don't let the myths stand in your way, get the facts.
Read article
How dangerous is the mysterious Rorschach ransomware?
Check Point Research uncovered a new, unbranded ransomware strain with record encryption speeds and rare evasion features. Just how dangerous is it?
Read article
Why you should take a risk-based approach to cyber security
Cyber security frameworks reduce breach risk, but a checklist mentality goes against a security programme's primary goal: reducing risk.
Read article
Why 2023 is the year to go agentless
Network growth is accelerating and security is struggling to keep up. Here's why agentless asset discovery is the elegant solution for 2023.
Read article
Cyber security frameworks: safeguarding businesses
A cyber security framework helps your organisation manage the risks and vulnerabilities of cyber threats with clear, consistent security guidelines.
Read article
Why asset management is critical
As the world becomes increasingly digital, effective IT asset management has never been more critical. Here are four reasons why getting it right matters.
Read article
Reduce ransomware by 86%?
Impressive percentages grab headlines, but statistics can mislead. We look past the numbers at the simple, effective steps that genuinely reduce ransomware risk.
Read article
Artificial Intelligence (AI) and Cyber Security
A lot of hype surrounds AI. This post looks at what it can mean for cyber security, the pros and cons of deploying it, and how it pairs with traditional defences.
Read article
New Year: New Advice?
State-sponsored cyber-threats are back in the headlines. CISA's Insights bulletin reminds us how much can be achieved with five simple, cost-effective steps.
Read article
86% of business owners believe digital risk will continue to grow
Many businesses fear a breach but lack the skills, technology and resources to respond. Simplified frameworks like Cyber Essentials offer a practical route to better defences.
Read article
Saving on network maintenance contracts
Most vendors require a support contract for security patches, yet a reliable equipment inventory is hard to maintain. A real-time view helps right-size your maintenance spend.
Read articleHuman error is behind most of the successful cyberattacks on businesses
Even security-aware employees still click suspicious links. So how can you protect your business against your own users? The answer lies in holistic network monitoring.
Read articleNo articles in this topic yet.